DNS Lookup — Query Any DNS Record Type for Any Domain
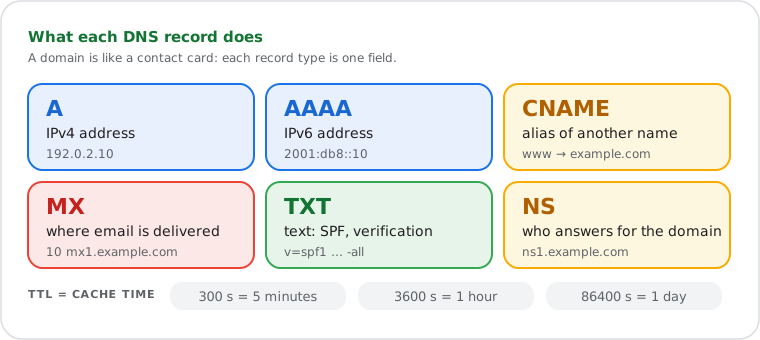
A DNS lookup asks what a domain points to: A and AAAA records give its IP addresses, MX its mail servers, NS its name servers, and TXT its text records such as SPF.
DNS lookup is the process of querying a Domain Name System (DNS) server to retrieve the
resource records configured for a domain name. Supported record types include A (IPv4 address),
AAAA (IPv6 address), MX (mail exchange), NS (name server), TXT, CNAME (canonical name alias),
SRV (service locator), and SPF. Each result includes the record value, name, and TTL —
the number of seconds the record may be cached by downstream resolvers, as defined in RFC 1035.
Protocol
UDP (RFC 1035), 3-second timeout per resolver
Record Types
A, AAAA, MX, NS, TXT, CNAME, SRV, SPF, PTR
Resolvers
Google 8.8.8.8 · Cloudflare 1.1.1.1 · OpenDNS 208.67.222.222 · Quad9 9.9.9.9 · Yandex 77.88.8.8 · Authoritative DNS
Caching
Disabled — every query is live
TTL
Returned in seconds (per RFC 1035)
How to Use the DNS Lookup Tool
1
Enter the domain name
Type a domain name into the input field — for example, google.com or mail.example.com. Do not include a protocol (http://) or path.
2
Select a record type
Choose ALL+ to retrieve all available record types in a single query, or select a specific type — A, AAAA, MX, NS, TXT, CNAME, SPF, or SRV.
3
Choose a DNS resolver
Select the server to query against: Google (8.8.8.8), Cloudflare (1.1.1.1), OpenDNS, Quad9, Yandex, or Authoritative DNS to query the domain's own name servers directly.
4
Click Lookup DNS Records
Submit the form. Results appear below, showing each record's type, name, value, and TTL.
5
Read the results
Each row shows one DNS record. The Value column contains the resolved data — an IP address for A/AAAA records, a hostname for MX/NS/CNAME, and text for TXT/SPF records. TTL is in seconds.
What the DNS Results Mean
Each row is one DNS record: its type, its value and its TTL, the number of seconds resolvers may keep it in cache.
Each record type is one field of the domain’s contact card.
Each row in the results table corresponds to one DNS resource record returned by the selected
resolver for the queried domain. The columns are defined as follows:
Column
Meaning
Example
Type
The DNS record type
A, MX, TXT, CNAME
Name
The domain or subdomain the record belongs to
google.com., mail.google.com.
Value
The record data — an IP address, hostname, or text string depending on type
The tool sends a live query to the resolver you choose (Google 8.8.8.8, Cloudflare 1.1.1.1, OpenDNS, Quad9) or to the domain’s authoritative name servers. “All records” asks for A, AAAA, CNAME, MX, NS, TXT, SOA and CAA one by one, because the old ANY query is no longer reliable (RFC 8482).
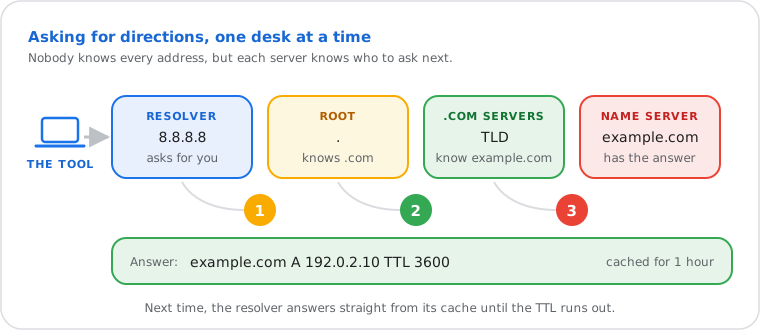
Each server knows who to ask next; the answer is then cached for its TTL. (Documentation addresses.)
The Domain Name System is a hierarchical, distributed naming system defined in RFC 1034
(concepts and facilities) and RFC 1035 (implementation and specification). When a DNS lookup
is performed, a UDP datagram is sent to the selected name server on port 53. The server
processes the query and returns the matching resource records, or an error code if no records
exist for that type.
Recursive resolvers — such as Google (8.8.8.8), Cloudflare (1.1.1.1), OpenDNS
(208.67.222.222), and Quad9 (9.9.9.9) — cache results up to each record's TTL and serve
cached answers to reduce load on authoritative servers. Authoritative name servers are the
definitive source for a domain's records: they never cache and always return the currently
published values.
When Authoritative DNS is selected, this tool performs a two-step resolution.
First, it queries Google 8.8.8.8 for the domain's NS records to discover its authoritative
name servers. Second, it resolves each name server to its IP address via an A record lookup.
Finally, it sends the actual DNS query directly to each discovered authoritative server —
replicating the behavior of a cold-cache resolver with no prior knowledge of the domain.
Do it yourself
How to Run a DNS Lookup Without an Online Tool
All major operating systems include command-line DNS tools. The online tool queries from a
neutral external resolver — results may differ from your local resolver due to caching.
dig google.com A
dig google.com MX @8.8.8.8
dig google.com TXT @1.1.1.1
dig google.com ANY
dig is the preferred tool for sysadmins and developers — it exposes the full DNS
response including TTL, response flags, and the authority section. On macOS, dig
is pre-installed. On Ubuntu/Debian, install it with apt install dnsutils.
Common Uses for DNS Lookup
Verifying a Domain Migration
A sysadmin migrating a site from one hosting provider to another needs to confirm that A
records have propagated before cutting over application traffic. Running the lookup against
both a recursive resolver and Authoritative DNS reveals whether old or new IP addresses are
being served — catching propagation gaps before users are affected.
Diagnosing Email Delivery Failures
A mail server administrator receives bounce reports citing DNS failures. Querying MX records
confirms which mail exchange servers are configured and in what priority order. If the MX
record points to a decommissioned server, the cause of delivery failures is immediately
visible without accessing the DNS control panel.
Validating Google Workspace and SPF Configuration
A developer setting up Google Workspace on a new domain queries TXT records to confirm that
both the Google site verification token and the SPF record (v=spf1) are correctly
published before enabling email sending. A missing or malformed SPF record causes messages to
fail DMARC alignment and land in spam.
Frequently Asked Questions
How accurate are the DNS results?
Results reflect the live response from the selected resolver at the time of the query. Recursive resolvers (Google, Cloudflare, Quad9, OpenDNS) may serve cached results up to the TTL of the record. Selecting Authoritative DNS bypasses all caches and returns the definitive current value directly from the domain's own name servers.
Why is my DNS record not showing up?
If a record was recently added or modified, recursive resolvers may still serve the old value until the TTL expires — typically between 5 minutes and 48 hours depending on the TTL the domain owner configured. Switch to Authoritative DNS in the resolver dropdown to see the current value regardless of cached data.
What is the difference between a recursive resolver and an authoritative name server?
A recursive resolver (such as Google 8.8.8.8 or Cloudflare 1.1.1.1) finds the answer by querying other DNS servers on the client's behalf and may return cached results up to the record's TTL. An authoritative name server is the definitive source for a domain's records — it never caches and always returns the currently configured values directly.
What does TTL mean in the results?
TTL stands for Time To Live and is specified in seconds, as defined in RFC 1035. It is the maximum duration a downstream resolver is permitted to cache the record before re-querying the authoritative name server. A TTL of 300 means the record may be cached for up to 5 minutes. A TTL of 86400 means up to 24 hours.
What does ALL+ query?
ALL+ queries A, AAAA, CNAME, MX, NS, TXT, SOA and CAA records one by one and shows them together. It does not use the DNS query type ANY: RFC 8482, published in January 2019, lets servers answer ANY with a minimal placeholder (often a single HINFO record), so ANY results are incomplete. SRV records need a service name (for example _sip._tcp.example.com) and are queried with the SRV button.
Do you store or log the domains I look up?
DNS queries are processed in real time to fetch the record from the selected resolver and are not stored or logged. No history of domain lookups is retained after the result is returned.